
Application Security – The Complete Guide

Source: https://www.udemy.com/course/application-security-the-complete-guide/What you’ll learn
- Learn how to become an application security champion.
- What is the OWASP Top 10 and how to defend against those vulnerabilities.
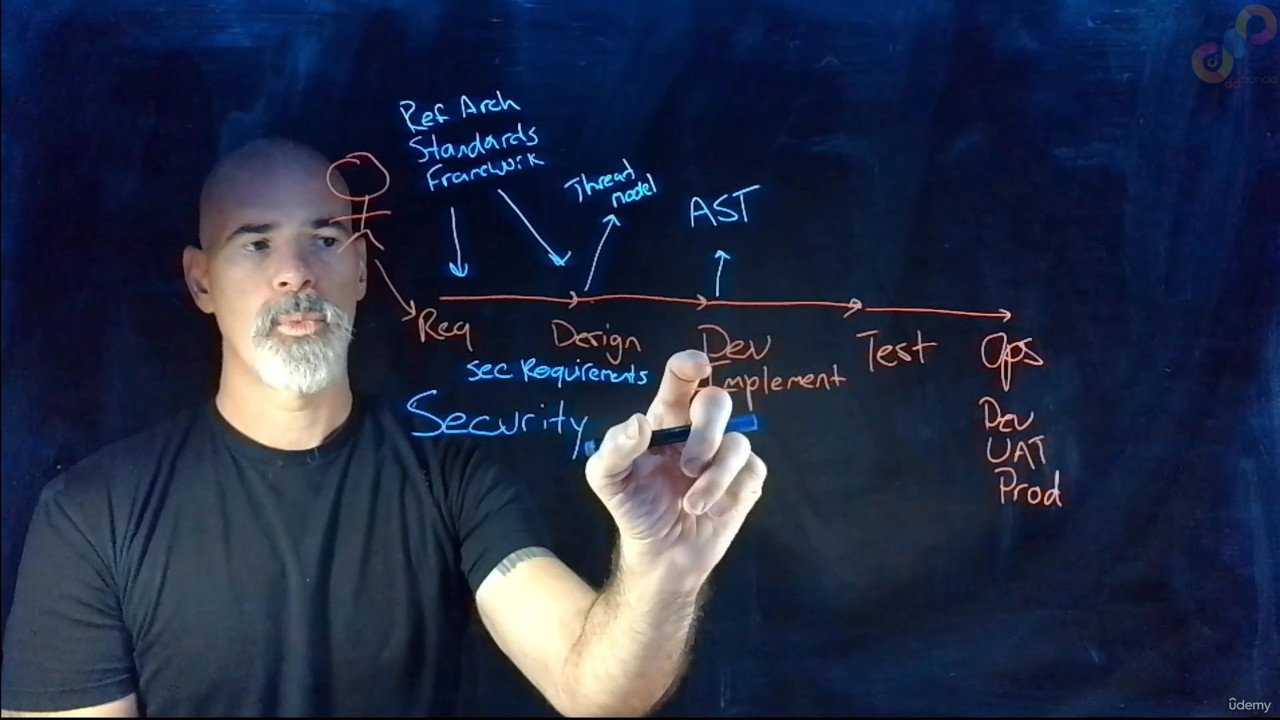
- Use of threat modeling to identify threats and mitigation in development features.
- How to perform a threat model on an application.
- How to perform a vulnerability scan of an application.
- Rating security vulnerabilities using standard and open processes.
- How to correct common security vulnerabilities in code.
- How application security fits in an overall cyber security program
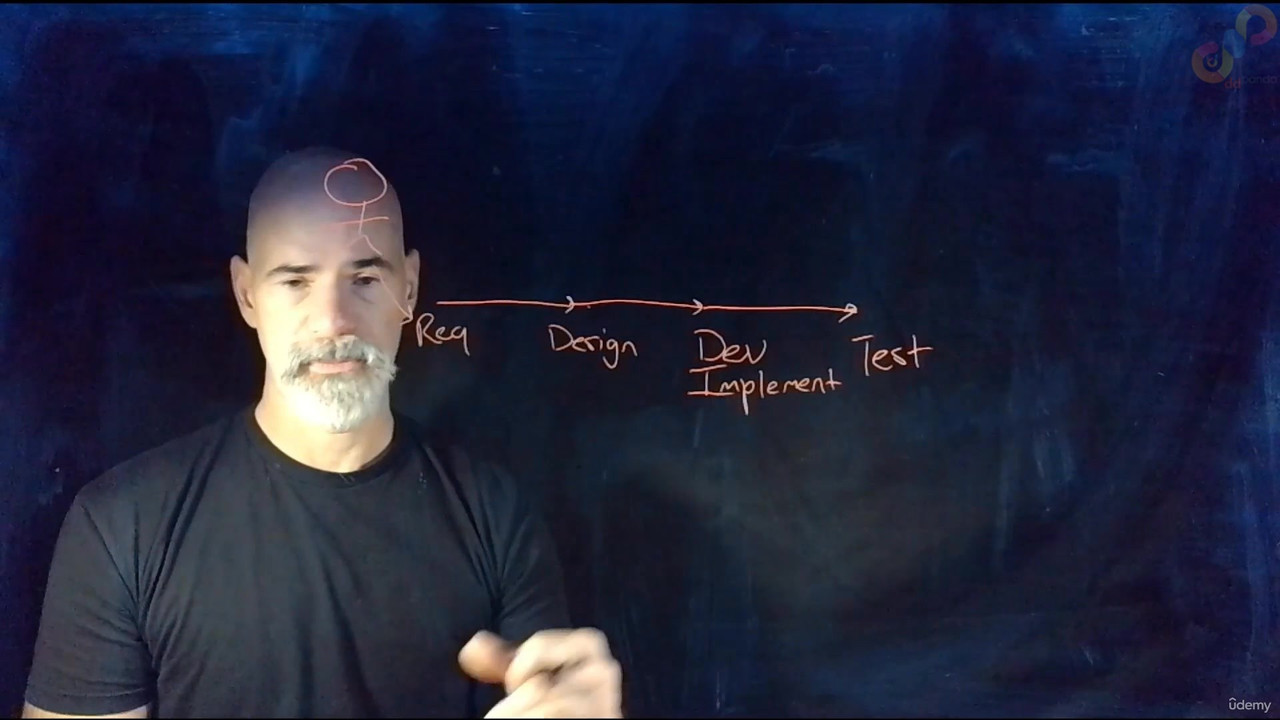
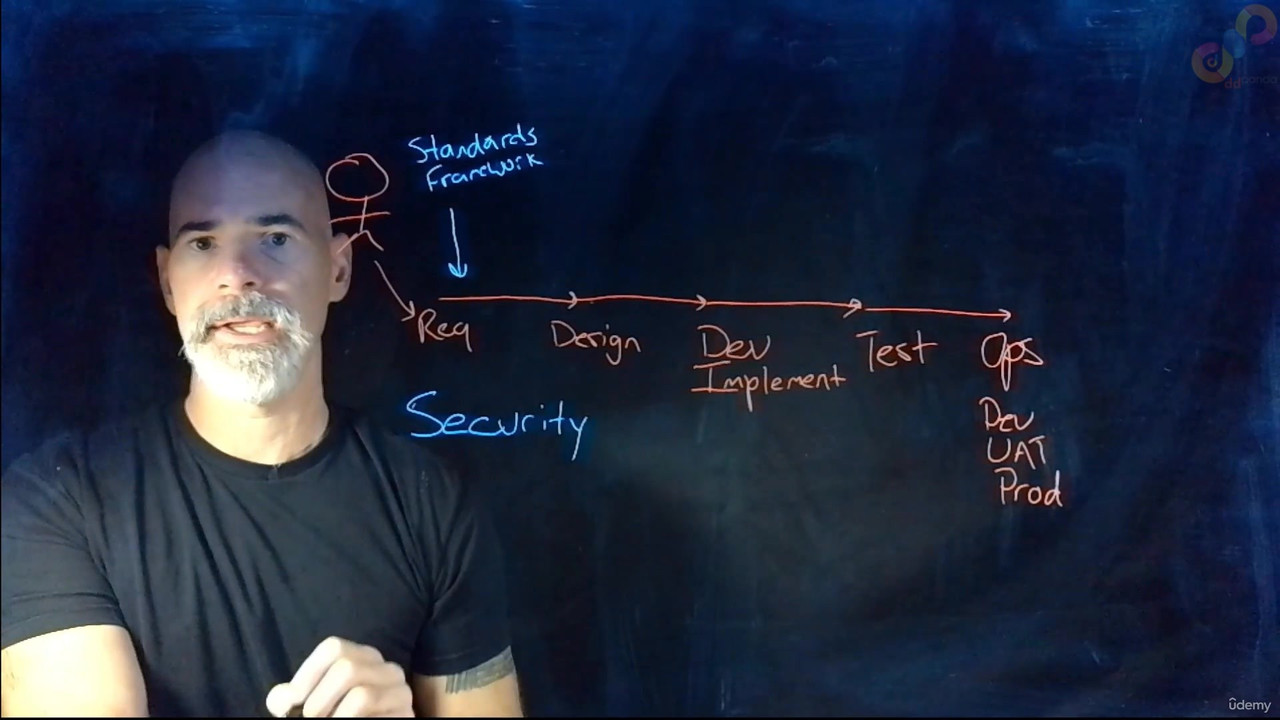
- Building security in to the software development life cycle.
Requirements
- Basic programming knowledge
- Understanding of IT systems and how software is deployed in operational environments
Download Links
Password: cms.ddpanda.org
Related Courses & Lessons
Keep learning from this topic

AI Reverse Engineering with OpenClaw and MCP
Use OpenClaw agents + Model Context Protocol (MCP) to automate debugging, disassembly and malware analysis with AI

Metasploit Framework: Penetration Testing with Metasploit
Become Hacker: Learn ethical hacking and penetration testing using Metasploit and start your cyber security career

Certificate of Cloud Security Knowledge (CCSK)
CCSK (Certificate of Cloud Security Knowledge) — a reputable international certification confirming a deep understanding of cloud technology security principles.

MAoS – Malware Analysis on Steroids
MAoS – Malware Analysis on Steroids with hands-on training in advanced malware analysis, unpacking, evasion techniques, and stealthy behavior tracking.

Cybersecurity Hands-On Labs: Hacking & Defense
Master cybersecurity through hands-on labs with Kali Linux, Nmap, Wireshark, SQLi, XSS, Active Directory, and more.

Security+ Fun: Pass the Exam, Learn the Job
A fun, beginner-friendly Security+ course with real-world examples, hands-on explanations, and exam-focused teaching.